
Security Review
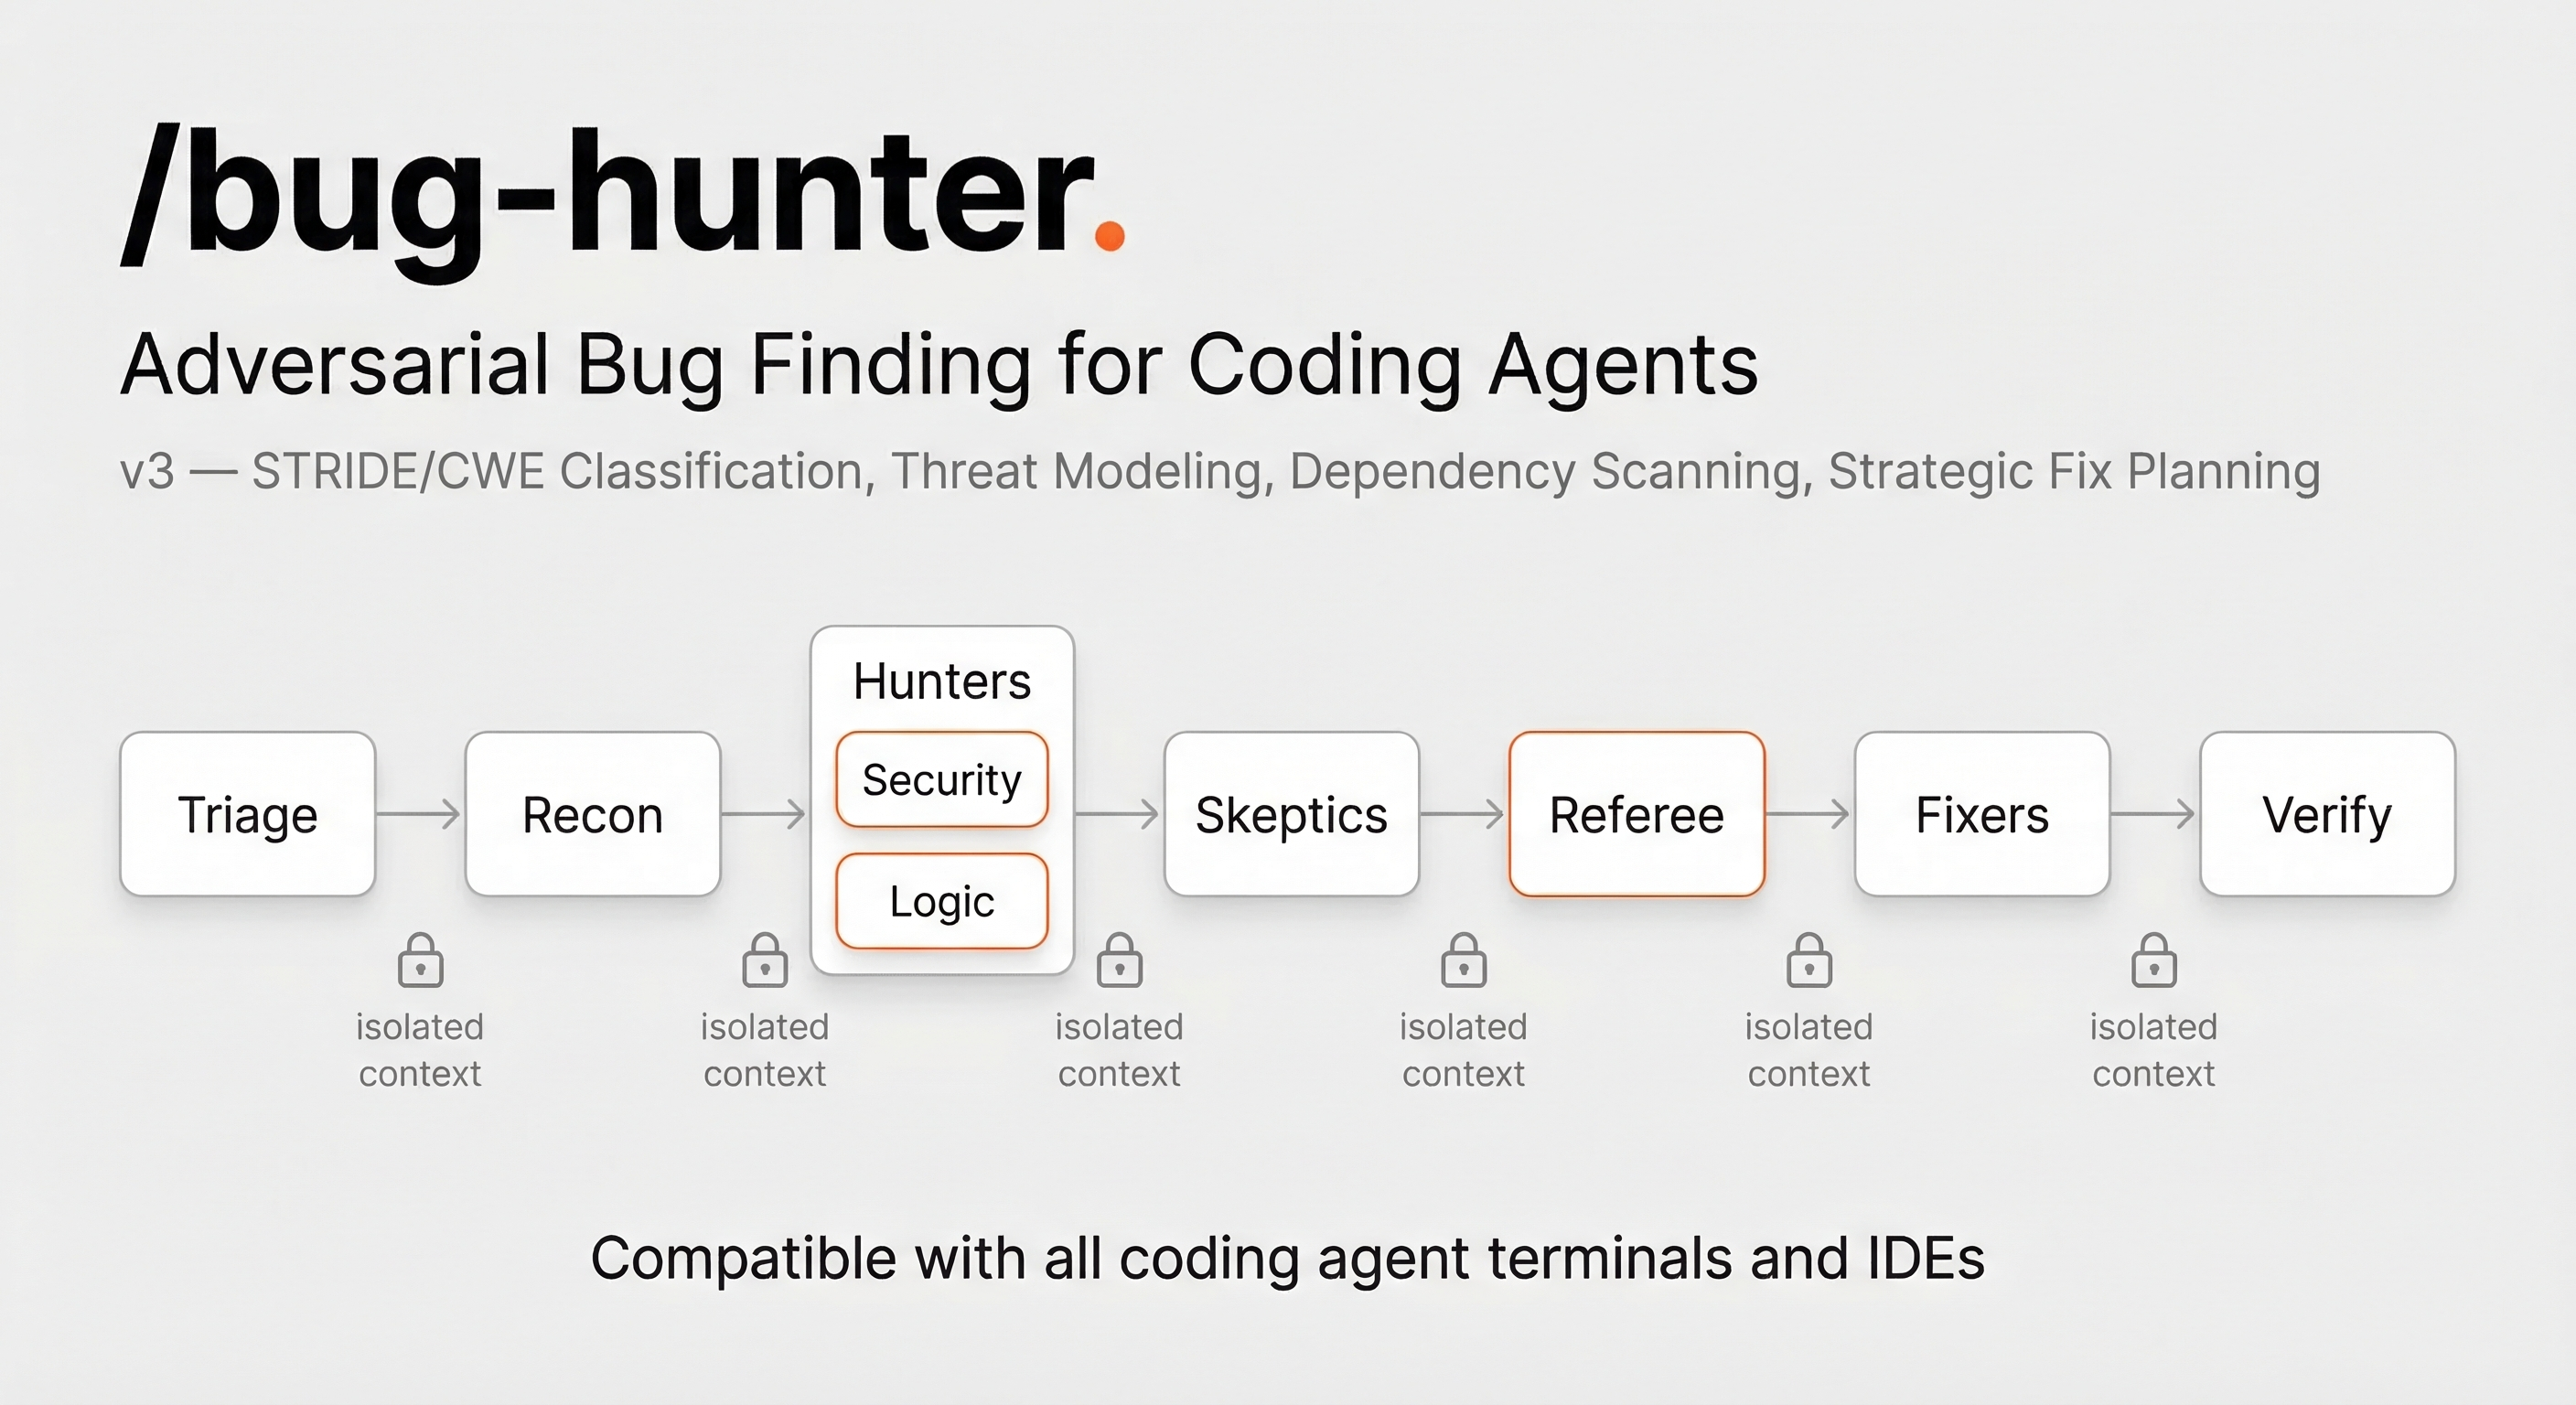
This is a bundled local Bug Hunter companion skill. It packages a security-focused review workflow without introducing any external marketplace dependency.
Purpose
Use this skill for deeper security audits than a simple bug hunt, especially when the user wants:
- a full security review
- PR security validation
- weekly security scanning
- dependency reachability + code review together
- threat-model-driven analysis
Workflow
Ensure
.bug-hunter/threat-model.mdexists.- If missing, invoke the bundled
threat-model-generationskill.
- If missing, invoke the bundled
Determine the scan mode from the request:
- PR → diff-scoped review via
commit-security-scan - staged → staged-only security review
- weekly → recent commit range on the default branch
- full → full repository security audit
- PR → diff-scoped review via
If dependency scanning is relevant, run:
node scripts/dep-scan.cjs --target <path> --output .bug-hunter/dep-findings.json
Scan code for STRIDE threats using Bug Hunter-native conventions. Reuse:
.bug-hunter/triage.json.bug-hunter/threat-model.md.bug-hunter/security-config.json.bug-hunter/dep-findings.json
Validate severe findings using the bundled
vulnerability-validationskill.Produce structured outputs compatible with the Bug Hunter pipeline.
Outputs
Primary artifacts should stay inside .bug-hunter/:
.bug-hunter/hunter-findings.json.bug-hunter/referee.json.bug-hunter/report.md.bug-hunter/dep-findings.jsonwhen dependency review is enabled.bug-hunter/fix-strategy.jsonif the user wants remediation planning
Important constraints
- Keep all paths Bug Hunter-native; do not emit
.factory/*artifacts. - Prefer validated, exploitability-aware findings over raw volume.
- For patching requests, hand findings back to the normal Bug Hunter fix pipeline rather than inventing a second patch system.